 LotsAgent
Security
9 posts
Not every agent action needs human approval — but some must. Here's a practical framework for configuring review gates in AI agent workflows.
Most AI agents run without identity or audit trails. Here's what proper AI agent security looks like when both are non-negotiable.
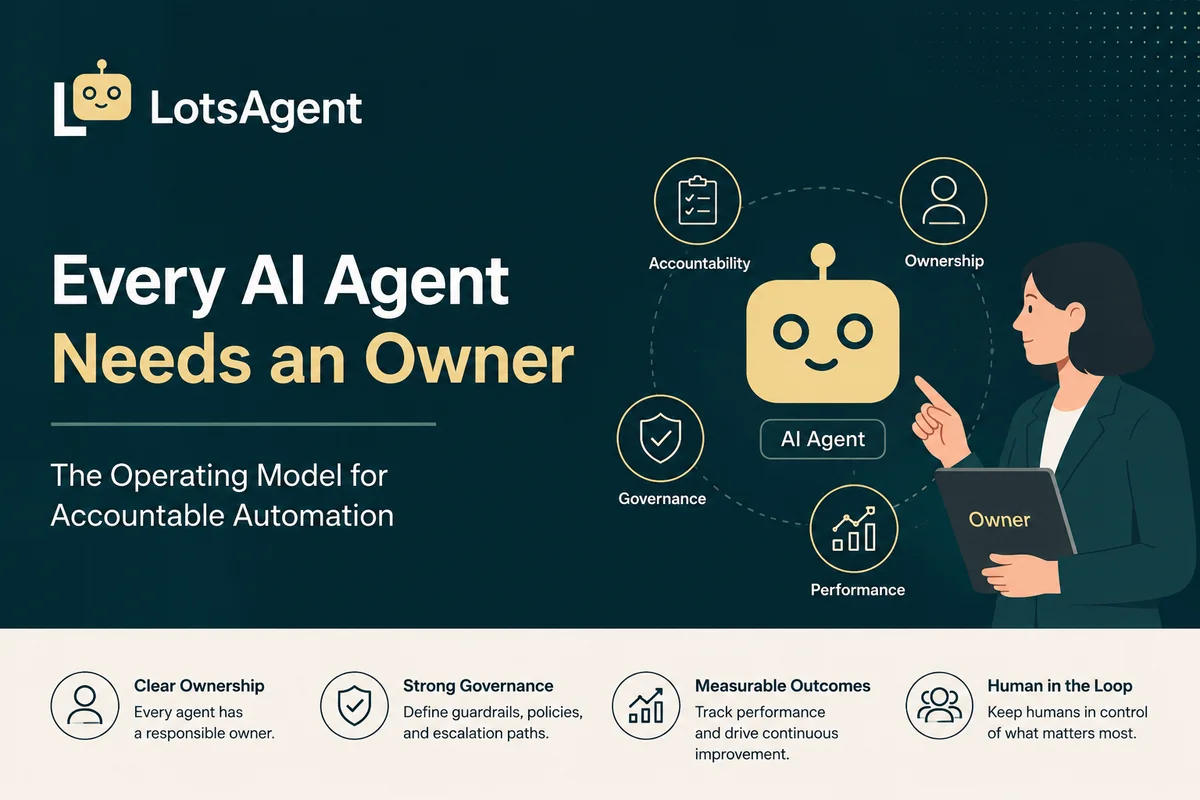
An owned AI agent has five things: identity, scope, review, audit trail, escalation. Here is the operating model that makes them accountable, with a 30-minute audit and the named-human questions every team should answer.

88% of AI agents fail post-pilot. Here's why DevOps practices for agents are no longer optional — and what the reliable AI stack actually requires.

Most AI agents fail silently, not loudly. Here's the 30-minute audit that catches 90% of production failures before your agent runs unattended — with real failure data and step-by-step checks.
Anonymous agents are a liability, not a feature. Here's why accountability — identity, audit trails, and kill switches — isn't optional in production AI agent deployments in 2026.
90% of AI agents fail in production within 30 days. Here are the 5 silent killers destroying deployments — and how to fix them before it's too late.
Your AI agent is running without an identity. Here's why that's a security nightmare — and how to fix it before 2026 becomes the year of AI agent accountability.
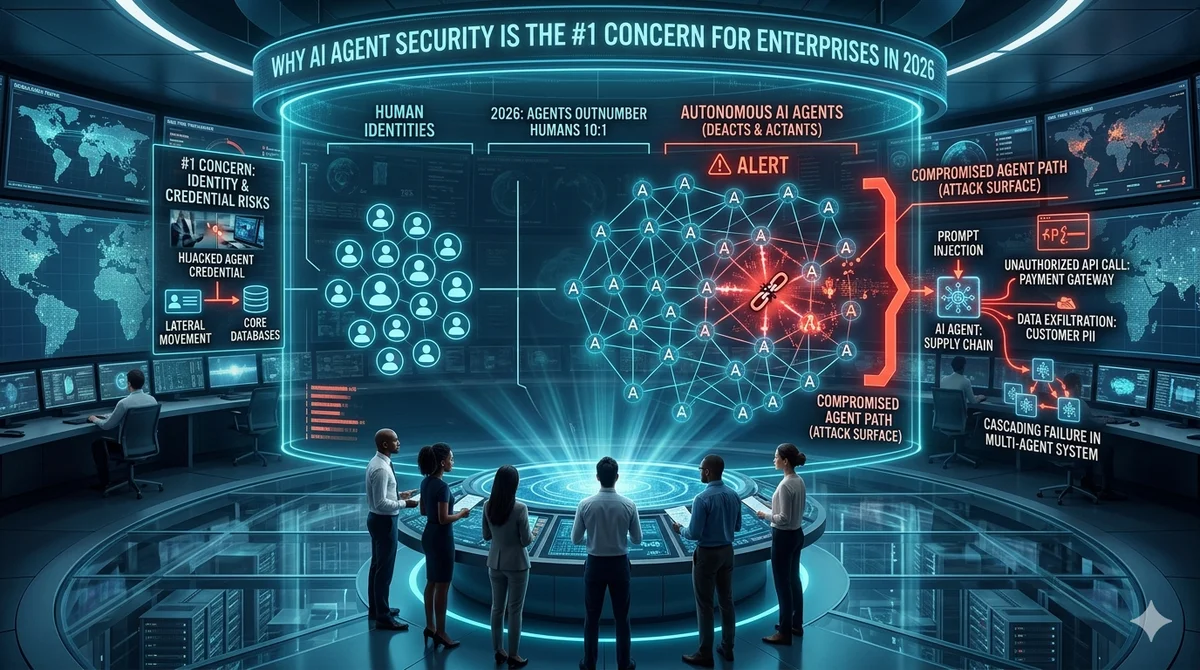
AI agent security in 2026: the three real threats, the OWASP and MITRE ATLAS frameworks, and an 8-step playbook for shipping agents that don't wreck your stack.